- A flaw in Telegram Desktop versions up through 7.2.8 enabled remote arbitrary file reading and account takeovers via a single clicked link.
- Discovered by security researcher beaksec, the exploit stems from unescaped semicolon character separators in Telegram’s internal IPC socket protocol.
- Telegram patched the High-severity vulnerability (CVSS 8.1, CVE-2026-107181) in version 7.2.9, urging all users to update instantly.
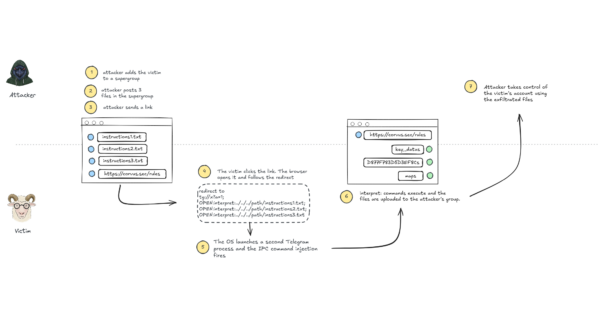
Security research has uncovered a severe exploit targeting Telegram Desktop users that could allow attackers to quietly hijack accounts with a single link click. Discovered by security researcher beaksec, the vulnerability (CVE-2026-107181) leverages an Inter-Process Communication (IPC) injection vector to read arbitrary local files from a victim’s computer and exfiltrate their login files directly to an attacker-controlled chat.
The vulnerability centers on how Telegram Desktop handles custom `tg://` URI schemes when the application is already running in the background. When a user clicks a link, the operating system spawns a new Telegram process. Finding an existing instance already running, the new process converts the link into a string of text and sends it over a local socket connection to hand off execution.
Telegram’s internal serialization format uses keywords followed by arguments and closes each command with a semicolon delimiter (e.g., `OPEN:tg://…;`). However, the application failed to escape semicolons contained inside the URL parameter itself. By embedding a semicolon into a crafted link, an attacker can trick the primary Telegram instance into splitting the string into multiple commands, executing instructions that were never intended by the source process.
While basic command injections could force the client to quit, combining this flaw with an internal `interpret:` URI scheme elevates the attack to full exfiltration. By injecting an `OPEN:` command into the socket, the exploit forces Telegram to read internal login session files without user confirmation and pass them straight to the attacker.
The flaw affects Telegram Desktop up to version 7.2.8 and was confirmed on Windows (version 6.9.3) with a High severity score of 8.1 (CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:U/C:H/I:H/A:N). Telegram has addressed the exploit in desktop release 7.2.9 (commit db3405699f), and users are advised to update immediately.
Source: Original Coverage
Leave a Reply